Web & data
Mobile App Developer Hiring Mistakes
Most failed app projects were lost at the hiring stage. See the nine mistakes that cause rebuilds and the questions that expose them before you sign.
A failed mobile app rarely announces itself on signing day. It appears months later as a build that runs on one developer’s phone, cannot pass store review, loses data when connectivity drops and costs more to hand over than anyone expected. By then, the buyer has paid for code without acquiring a maintainable product.
The nine mistakes below are visible before a contract is signed. Each section shows what the mistake looks like, the cost it creates and the question that exposes it. The questions do not turn a founder into an engineer; they make the selection process accountable. OVELITHUB’s related web development services use the same ownership, testing and handover discipline for browser-based systems.
Why app failures are often hiring failures
The dangerous supplier is not always the least experienced one. It can be the person who agrees to every feature, deadline and budget without identifying a conflict. A useful developer pushes back early: offline operation changes the data model; account deletion affects several systems; a sensitive permission may lengthen review; a promised launch date leaves no room for external approval. Disagreement at scoping is often evidence of care.
Buyers tend to evaluate what they can see: polished screens, a confident presentation and a single total price. Maintainability lives elsewhere—in repository history, automated checks, account control, deployment documentation, backend design and the ability of a second engineer to understand the system. If those are absent, the next budget starts by reconstructing decisions or replacing the code.
Mistake one: buying a price instead of a scope
What it looks like: a vendor gives a fixed total after a short call and a feature list such as “profiles, chat, payments and notifications.” The quote does not describe roles, edge cases, supported devices, integrations, migration, accessibility, analytics, security, acceptance or release work.
What it costs later: every unstated behaviour becomes an argument. The buyer believes it was implied; the supplier calls it a change. A low quote then grows through change requests, or the team protects the price by shipping the narrowest interpretation. Comparing totals is meaningless when quotes describe different products.
Ask: “What is explicitly excluded from this price, which assumptions could change it, and what evidence will demonstrate acceptance?” A good answer names exclusions without embarrassment, breaks the estimate into traceable areas, identifies uncertain work and proposes a discovery step where uncertainty is too high for a defensible commitment.
Mistake two: never asking who owns the code and accounts
What it looks like: the supplier keeps the only source repository, registers cloud services under a personal email and publishes through its own store accounts. The client receives a build file, not administrative control. This may feel convenient during development and become a hostage situation during disagreement, absence or insolvency.
What it costs later: another team cannot deploy, rotate credentials, review history or submit updates. Transfers are possible in some circumstances but add policy, identity and timing risk. Apple states that the person who enrols becomes Account Holder and that an organisation’s Account Holder manages renewal and legal agreements in its developer roles documentation. Google recommends adding supplier users rather than sharing the owner’s login in its developer-account security guidance.
Ask: “Which legal entity will own the source, design files, store listings, domains, signing assets, cloud resources and third-party accounts, and when will we receive access?” A good answer puts client-owned assets in client-controlled organisations from the start, assigns named roles, prohibits shared passwords, defines intellectual-property transfer and includes an exportable handover inventory.
Mistake three: judging a portfolio you cannot verify
What it looks like: a deck shows attractive screens but not a live listing, current version or the supplier’s exact contribution. Agencies sometimes present work delivered by former staff or show an app for which they built only a small component. A static screenshot says nothing about stability, update history or operational ownership.
What it costs later: the buyer selects for visual presentation while assuming competence in authentication, payments, synchronisation, accessibility and release operations. Those capabilities were never demonstrated.
Ask: “Show me two apps still live, explain exactly which parts your proposed team built, and walk me through a difficult post-launch change.” Check the publisher, version history, recent reviews and whether the described features exist. Ask for a reference whose project resembles yours in risk, not merely in colour. If confidentiality prevents public disclosure, request a redacted architecture or a live explanation of decisions and trade-offs.
Mistake four: accepting no answer on testing
Expect a device and quality plan
What it looks like: the proposal says “QA included” without naming who tests, what is tested, which devices and OS versions matter, how defects are recorded or what must pass before release. An emulator is useful, but it cannot reproduce every camera, biometric, notification, memory, radio, manufacturer or performance condition.
What it costs later: common paths work in a developer environment but fail for real users. Each release reopens old defects because there is no regression suite—the repeatable set of checks confirming that previously working behaviour still works.
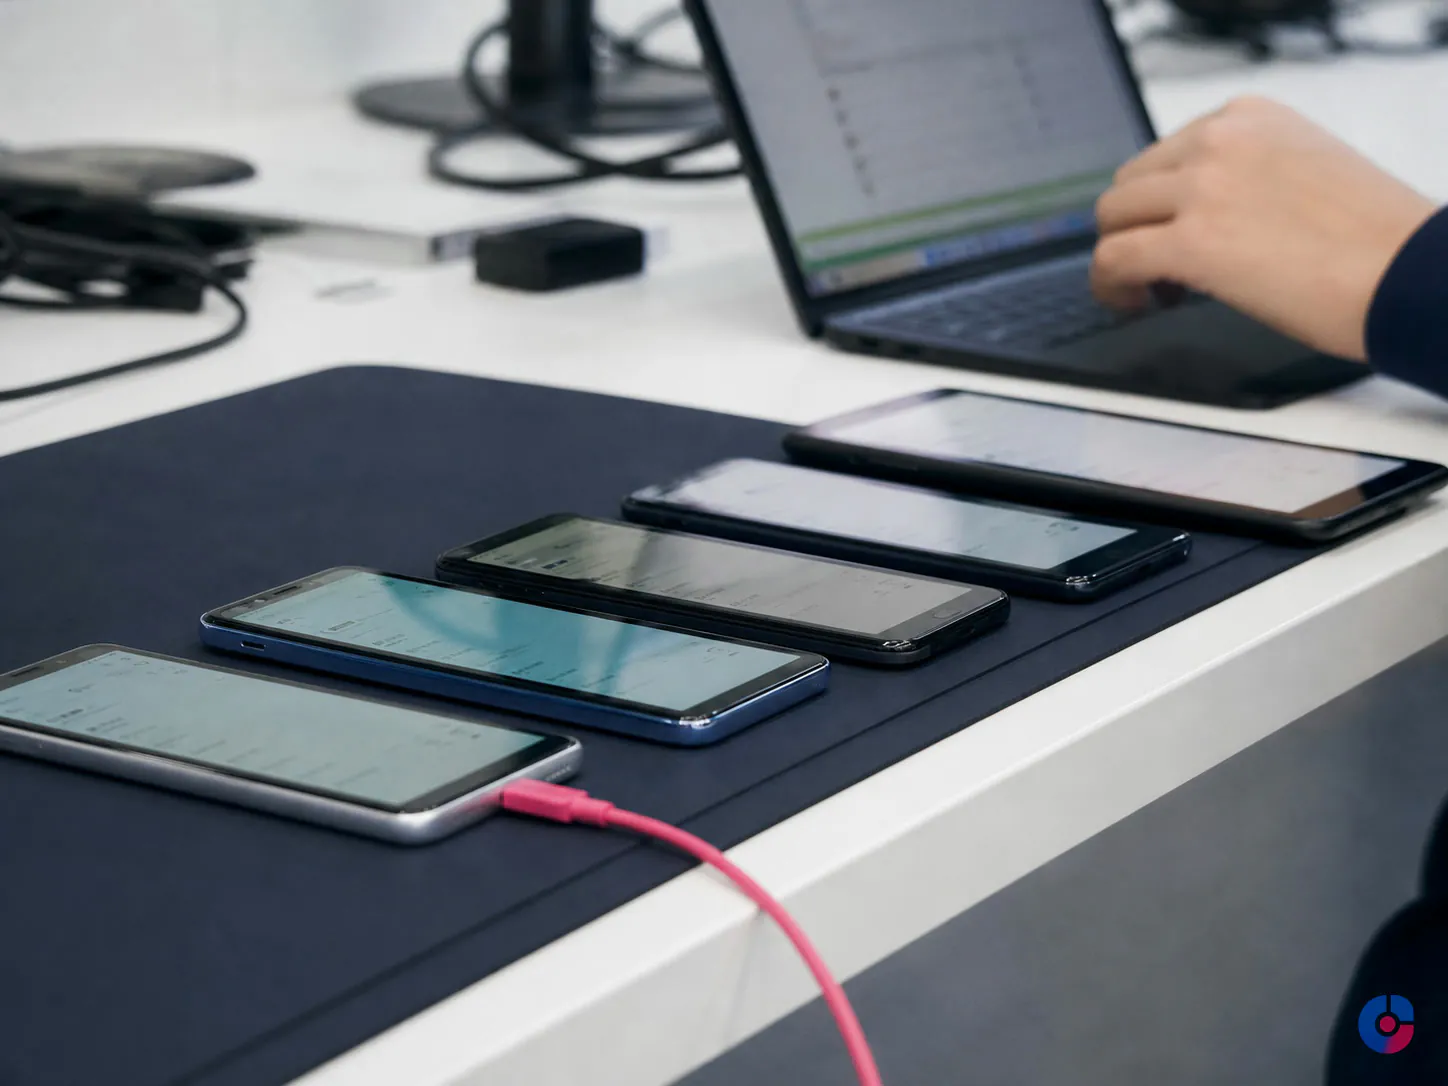
Ask: “Show the proposed test matrix, one sample test case and the release gate.” A good answer combines automated and exploratory checks, tests important flows on real devices, covers supported OS versions, includes poor connectivity and interruption where relevant, and gives the buyer access to a defect tracker. Coverage should be based on the audience and product risk, not an arbitrary promise to test everything.
Define responsibility after launch
A warranty is not the same as maintenance. The contract should define a defect as behaviour that fails an agreed requirement or acceptance condition. A new workflow, changed store rule or revised business need is a change request. State the warranty period, severity levels, response expectations, supported production version and process for reproducing and fixing an issue.
Ask: “Which production problems are corrected within the build fee, for how long, and how will you decide whether something is a defect or a change?” A good answer uses written acceptance evidence and does not promise that every future problem is free.
Mistake five: ignoring the backend and data model
What it looks like: every conversation centres on screens. Nobody explains where authoritative data lives, how users authenticate, how devices synchronise, what happens offline, how conflicts are resolved, how APIs change or how data is migrated. Yet most useful apps depend on services outside the phone.
What it costs later: duplicate records, lost changes, slow screens, brittle integrations and a backend that cannot support the next release. Changing a data model after real customers exist requires migration, compatibility and rollback work. That can be harder than changing the interface.
Ask: “Trace one critical record from creation on the phone through the API and database, then explain offline behaviour, conflict resolution, versioning, backup and recovery.” A good answer distinguishes the system of record, states what is cached, names failure states and explains how an old app version behaves after the backend changes. It should also assign responsibility for hosting, monitoring, security updates and incident response.
Mistake six: choosing technology before requirements
What it looks like: the vendor recommends native iOS and Android, Flutter, React Native or another framework before learning what the app must do. Often it recommends the stack it already sells. Technology preference is understandable; presenting it as a universal product truth is not.
What it costs later: the buyer either pays for unnecessary platform-specific work or discovers that a shared codebase needs custom native modules for performance, new OS capabilities or a difficult third-party SDK. Cross-platform development can reduce duplicated work, but it is not automatically cheaper after testing, integration and long-term upgrade costs.
Ask: “Which product requirements drive this recommendation, what will remain platform-specific, and what would make you choose the alternative?” A good answer weighs performance, offline complexity, interface expectations, hardware access, accessibility, release pace, available maintainers and dependency risk. Request a short architecture decision record so future teams know why the choice was made.
Mistake seven: leaving store review and compliance until launch
What it looks like: review is treated as a final upload task. The team has not planned privacy disclosures, account deletion, demo access, permission justification, payment rules, age classification, content moderation or regional obligations.
What it costs later: a launch date depends on an external review that exposes a product-level issue. Replacing a login, payment or permission flow at that point is not packaging work. Apple says submissions should be final, tested on-device and accompanied by complete metadata and reviewer access in its App Review Guidelines. Those June 2026 guidelines also require accessible privacy policies and, for apps that support account creation, in-app account deletion.
Google’s current prepare-for-review guidance requires relevant App content declarations and reviewer access instructions. Its Data safety documentation requires developers to declare how published apps collect, share and protect data. Policies change, and some categories or permissions add requirements, so review the live documents for each release.
Ask: “Which current Apple and Google rules affect this product, who owns each declaration, and how much schedule contingency covers review or rejection?” A good answer includes compliance checks in discovery, tests a release candidate, prepares durable reviewer credentials and assigns a person to respond. Legal advice is needed where privacy, health, finance, children or regulated services raise obligations beyond store policy.
Mistake eight: treating launch as the finish line
What it looks like: the budget ends when version 1.0 is approved. There is no owner for monitoring, analytics, crash review, customer support, OS compatibility, dependency updates, certificate management, backups or incident response.
What it costs later: a working product decays. Operating systems, SDKs and store rules change; vulnerabilities emerge; certificates expire; third-party APIs deprecate; real users reveal behaviours the test plan missed. Maintenance is not proof of a bad build. It is part of owning software.
Ask: “What recurring work will this app require during its first two years, who performs it and how is it budgeted?” A good answer separates monitoring and routine upgrades from enhancements, defines support coverage and exit terms, keeps dependencies inventoried and gives the client access to analytics and operational alerts. Support processes may also need trained responders; the principles in platform troubleshooting support apply once users depend on the product.
Mistake nine: hiring one person for a team-shaped job
What it looks like: a single person is expected to discover requirements, design interfaces, build two clients and a backend, secure infrastructure, test devices, manage stores and support production. A talented generalist can cover several areas, but simultaneous specialist risk does not disappear.
What it costs later: there is no independent review, progress stops during absence and knowledge lives in one head. This “bus factor” is the number of people who can disappear before the project becomes unable to continue. A value of one is a business-continuity decision, not merely a staffing choice.
Ask: “Who will perform architecture, implementation, code review, QA, release and support, and who covers each role during absence?” A solo developer can be the right choice for a tightly bounded prototype, internal tool or product with a technically capable client owner. A small agency or managed team suits a maintained production app when independent QA, review and continuity justify the cost.
That model has an honest trade-off: a managed team with QA and code review normally costs more per hour than a lone freelancer. It is worth paying only when the app’s lifespan, operational impact and change rate make continuity valuable. Compare the total capability and ownership model, not just hourly rates. Related guidance on evaluating a supplier is available in how to choose a web development company.
A due diligence checklist for one vendor call
- What is excluded, assumed and still uncertain in this scope?
- What evidence must exist for each major feature to be accepted?
- Which entity owns every repository, account, design, dataset and deployment asset?
- Which live products did the proposed team build, and which parts were theirs?
- What devices, OS versions and failure conditions will be tested?
- How are warranty defects distinguished from new requirements?
- Where is authoritative data stored, and what happens offline or during conflict?
- Which requirements determined the technology choice, and what are its known compromises?
- Which store, privacy and permission requirements affect the proposed features?
- What work and budget keep the app supported after launch?
- Who reviews code and QA evidence, and who covers absence?
- What exactly will another competent team receive at handover?
A good supplier answers with artefacts: a scope sample, risk register, repository permissions, test matrix, architecture note, release checklist and handover inventory. “We handle all of that” is reassurance, not evidence. The buyer should also ask to meet the people assigned to the work rather than evaluating only the salesperson.
Keep reading
Related insights
Shopify Store Support Services: A Guide
A Shopify store needs weekly upkeep, not occasional fixes. See the support tasks that protect revenue, who should own each, and what…
Shopify vs WooCommerce: Which to Choose
Shopify and WooCommerce both work. The difference is who carries the maintenance and where the cost lands. Compare both against your team…
How to Choose a Web Development Company
Choosing a web development company in the USA or Europe? Use these nine selection criteria to judge proposals, ownership terms and post-launch…