Support & sales
Cold Email Deliverability Checklist
Most cold email fails before it is read. See how to protect deliverability, build a list that stands up, and run outreach that respects the rules.
The campaign that had a copy problem and an infrastructure problem
The first sequence receives some replies. Each week after that, measured opens fall, replies dry up and more messages bounce or land in junk. The team rewrites subject lines, adds personalisation tokens and buys another list. Nobody checks authentication, complaint signals, domain alignment or whether invalid addresses entered the sequence.
The apparent copy problem sits downstream of an infrastructure problem. If receiving systems reject, filter or distrust the message, the words never receive a fair test. Worse, reckless outbound from the primary business domain can affect ordinary customer, supplier, password-reset and employee mail.
The operating order is infrastructure, lawful list and suppression, then message. This makes cold email slower to start. The alternative is spending faster while damaging a domain and brand the business needs for normal communication.
Sending infrastructure before anything else
Design outbound with a qualified email administrator, legal or privacy review and current receiver guidance. Do not use lookalike domains that conceal the sender or impersonate another organisation. Where risk isolation is appropriate, use a clearly related, transparently branded sending domain or subdomain under company control, and preserve the trusted primary domain for core business mail. The right architecture depends on the organisation’s mail environment and applicable rules.
Provisioned mailboxes
Use named, monitored mailboxes with a real reply route, appropriate licensing, recovery controls and multi-factor authentication. Define who may send, triage replies, process objections and access history. Avoid disposable accounts that make identity unclear or leave conversations stranded when a worker exits.
SPF in one sentence
Sender Policy Framework publishes which mail systems are authorised to send for a domain. Keep one valid record, include every legitimate sender deliberately and remove services no longer used. SPF alone does not prove that the visible From address belongs to the authorised system.
DKIM in one sentence
DomainKeys Identified Mail adds a cryptographic signature that lets a receiving system verify an authorised domain signed the message and that signed content was not altered in transit. Protect and rotate keys under the mail provider’s current guidance.
DMARC in one sentence
Domain-based Message Authentication, Reporting and Conformance checks alignment between the visible From domain and authenticated SPF or DKIM domains, then applies a published policy and can produce reports. Start from an inventoried mail environment; an aggressive policy applied before all legitimate senders are aligned can block valid mail.
Google’s current Gmail sender guidelines require SPF or DKIM for all senders to personal Gmail accounts and SPF, DKIM and DMARC plus other controls for senders around the bulk threshold described in its documentation. Google’s FAQ says messages from the same primary domain count together and enforcement has increased. Microsoft’s current Outlook high-volume sender notice also specifies SPF, DKIM and DMARC requirements for domains over its stated daily volume to consumer Outlook services. Read the live pages before every material ramp; thresholds, scope and enforcement can change.
Authentication is necessary, not permission and not guaranteed inbox placement. Receiving systems also consider unwanted mail, complaints, content, list quality, volume pattern and other signals. Passing SPF, DKIM and DMARC does not make unsolicited sending lawful or welcome.
Warm-up and volume discipline
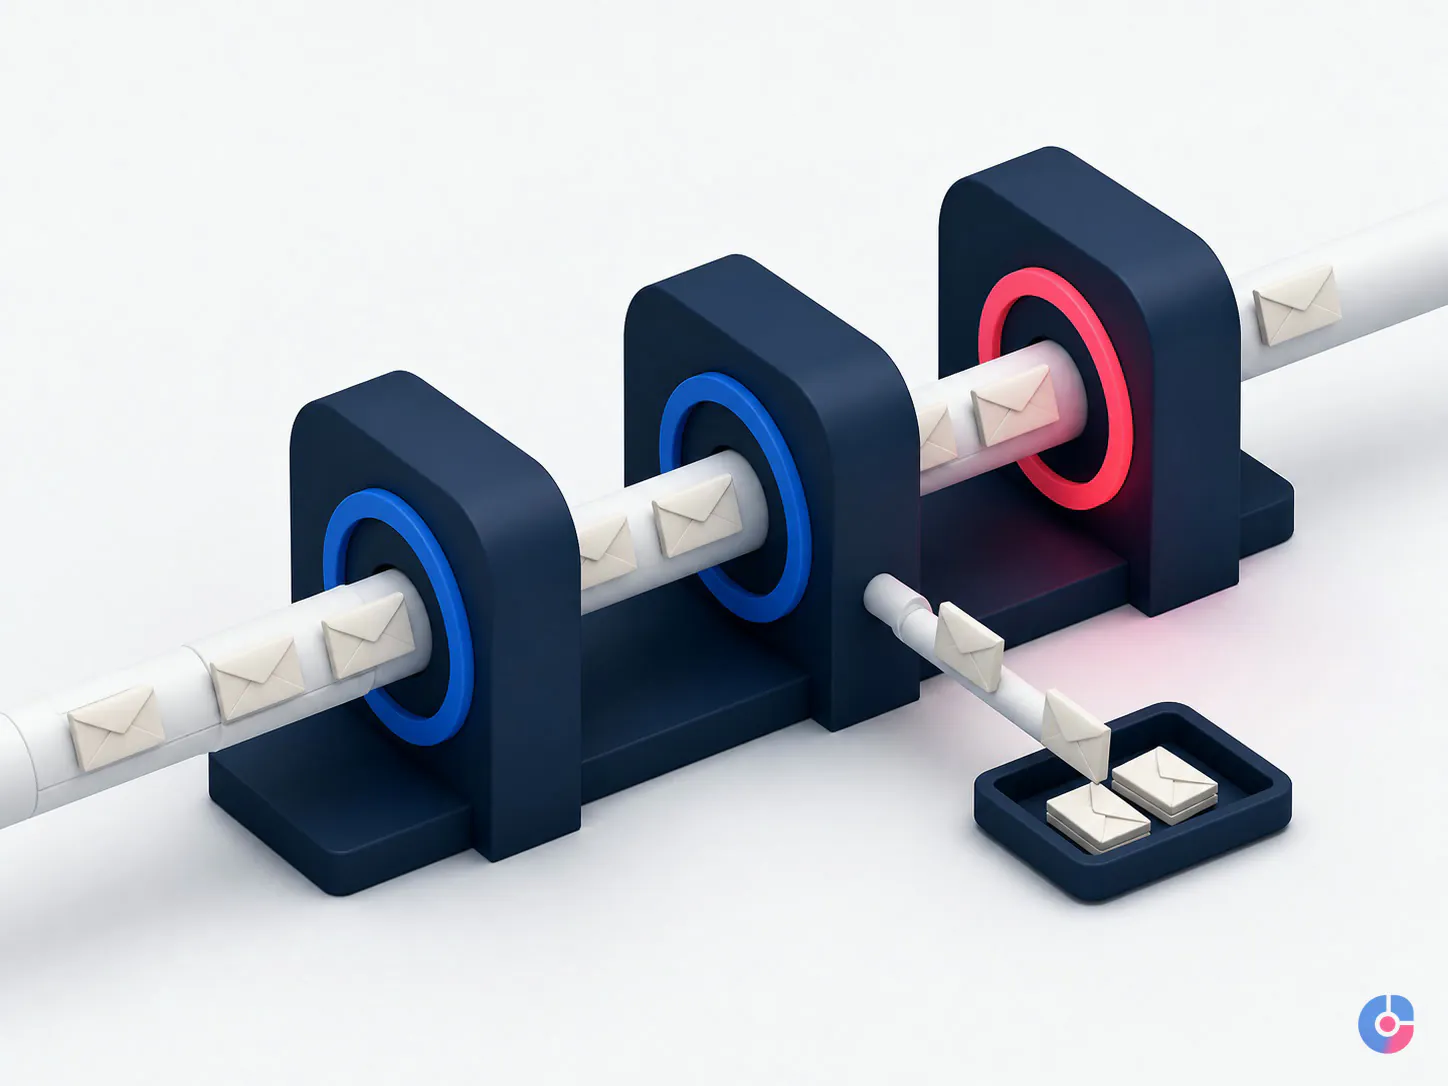
A new or newly repurposed sending identity has little observable history. Begin with real, relevant, low-volume communication to a lawfully selected audience and increase only after authentication, delivery, reply, complaint and provider feedback remain acceptable. There is no universal safe starting volume, daily increment or per-mailbox limit: providers, domains, recipients, message types, history and reputation differ.
Create a ramp sheet with date, mailbox, recipient domain mix, messages attempted, delivered, temporary failures, permanent failures, replies, positive replies, objections, complaints, blocks and provider notices. Define who can pause the sequence. Review by recipient domain because one receiver may reveal a configuration or reputation problem before the aggregate does.
Space human-scale messages according to the approved campaign rather than releasing a large batch at once. Respect the sending platform and mailbox provider’s current limits; those are ceilings, not deliverability targets. More mailboxes do not create more permission or reputation. Multiplying identities to bypass controls can magnify complaints and make governance impossible.
Pause when hard bounces, blocks, complaints, authentication failures or unexpected provider responses exceed the organisation’s written tolerance. Investigate the source and affected segment before resuming. Do not “warm” accounts through fabricated conversations, automated exchanges or messages to people who did not agree to receive them merely to manipulate reputation signals.
The list is the campaign
Begin with a segment small enough that one relevant reason for contact applies to every member. Define organisation type, geography, role, business situation, exclusion and the evidence that supports inclusion. A purchased or scraped list is not strategy, proof of accuracy or consent.
For every record, retain the source, source date, verification date, selection reason, jurisdiction, relevant lawful-basis or consent record where applicable, suppression status and reviewer. Verify that the business and role still exist and that the address is appropriate for the intended communication. Do not infer sensitive characteristics or collect excessive personal information to simulate relevance.
Address-validation tools can detect formatting, domain and some mailbox risks; they cannot prove a human wants the message, that the person remains in the role or that use is lawful. Catch-all domains require cautious treatment because the server may accept mail without confirming the named mailbox. Segment or exclude uncertain records according to the risk policy rather than calling them verified.
Maintain one suppression system across teams, domains and vendors. It should cover opt-outs, objections, complaints, known invalid addresses, customers or competitors excluded by policy and other do-not-contact reasons. Apply suppression before upload and again immediately before send. Preserve the minimum record needed to honour the request under applicable law.
Set a batch-level bounce stop rule before launch. The threshold should be materially below receiver or provider enforcement limits and reflect historical quality; document it rather than copying an industry number. A cluster of hard bounces pauses that source or segment. Remove invalid addresses, investigate how they entered and revalidate the remaining batch. Never keep retrying permanent failures.
Why narrow segments outperform large ones operationally
A narrowly defined segment allows one observation, problem and proof to remain true across the list. It also makes replies interpretable: a poor response can be traced to selection, message or offer. A message broad enough for two thousand unrelated people usually contains a generic claim and no defensible reason for contacting this person.
This is not a guarantee of higher reply rate. Smaller segments can still be wrong, the offer may be weak and the market may not want contact. The separate prospect research guide addresses the evidence layer in more depth.
Write to earn a reply
The first email should make four things clear in plain text: who is writing, why this person was selected, what relevant problem or outcome is being raised and what small response would move the conversation forward. Personalisation is not inserting a first name or recent post. Relevance is a reason that connects the recipient’s work to the message without pretending to know private circumstances.
- One relevant observation: a verifiable company or role fact tied to the segment, not flattery.
- One reason for contact: explain the operational issue or opportunity in language the recipient recognises.
- One bounded proof point: use approved, supportable experience or method; do not invent client results.
- One low-friction ask: a reply confirming relevance, owner or interest—not necessarily a meeting.
- One real signature: sender name, organisation, valid reply and required identification or contact information.
Keep the message as short as the idea allows. Avoid unexpected attachments, image-heavy designs, link clutter, deceptive reply prefixes and false familiarity. Plain formatting reduces distractions but does not create deliverability by itself. Review every claim and destination.
The goal of the first email is an honest reply. Asking whether the issue belongs to the person can be more appropriate than placing a calendar link immediately. Sales qualifies the conversation after interest; the outbound team should not disguise an appointment request as research.
Sequences, follow-up and knowing when to stop
Choose the number of touches and spacing according to market rules, sales cycle, recipient risk and brand tolerance. There is no universal sequence. Write the stop point before the first send and process any opt-out or objection immediately under the applicable requirement.
Each follow-up should add useful context or change the angle: clarify the problem, offer a short resource, ask whether another owner is appropriate or acknowledge that the timing may be wrong. Repeating “just following up” adds pressure without value. Do not move silently from email to personal phone, social account or another address without a lawful, policy-approved reason.
A clean closing message identifies the sender, acknowledges no response, leaves a simple way to engage and states that the sequence will stop. Then stop. An unbounded sequence increases complaint and brand risk and prevents the team from learning that the segment or offer may be wrong.
The rules differ by market
This section is orientation, not legal advice. Requirements depend on sender and recipient location, individual or corporate status, data source, relationship, message purpose and national implementation. Map jurisdictions and obtain qualified advice before list acquisition or sending.
United States
The FTC’s current CAN-SPAM guide says the Act applies to business-to-business commercial email. It covers truthful header and subject information, commercial identification, a valid physical postal address, a working opt-out and responsibility for a vendor sending on a company’s behalf. Federal requirements are not the only possible duties; assess state, sector and privacy law.
United Kingdom
The ICO’s B2B marketing guidance explains that PECR treatment differs by method and subscriber type; sole traders and certain partnerships receive treatment different from corporate subscribers. UK GDPR may also apply to named business contacts. The page currently warns that its guidance is under review following the Data (Use and Access) Act, so verify at campaign time.
European Union and EEA
The ePrivacy Directive addresses unsolicited direct-marketing email, including consent, existing-customer conditions, sender identity and a valid stop address, while treatment and protections for legal persons depend on national implementation. GDPR can apply when personal data is processed. Check the recipient country’s current law and regulator, not an “EU cold email” summary.
Canada
The CRTC’s current CASL guidance states that commercial electronic messages generally require consent, identification information and an unsubscribe mechanism, including messages sent to Canadian recipients from another country. Implied consent is limited and must be evidenced; a publicly visible address is not a blanket licence.
Across markets, identify the sender truthfully, maintain suppression, keep source and decision records, honour objections and review third parties. A sequencing tool cannot decide legal basis by detecting a country code.
Measure outbound honestly
- Attempted, delivered and bounce outcomes: separate temporary and permanent failures, recipient domains and source batches.
- Reply rate: use unique human replies divided by delivered messages under a documented rule; exclude automated responses separately.
- Positive reply rate: define positive, referral, timing, objection, negative and opt-out before classification; sample quality.
- Qualified conversations or meetings: apply the sales-accepted definition and attendance rule, not calendar invitations alone.
- Pipeline: connect accepted opportunities to source and cohort while acknowledging sales execution and market effects.
Treat open rate as diagnostic at most, not a performance measure. Apple’s Mail Privacy Protection documentation says remote content can be downloaded privately in the background when a message is received instead of viewed. Image loading, proxies, client settings and security systems can create apparent opens or hide real ones. Reply and business-outcome evidence is harder, but more meaningful.
Do not optimise around a benchmark without matching segment, region, message, provider, definitions and sample. Compare controlled cohorts and record changes to infrastructure, list, copy, sender and offer. A reply improvement after three simultaneous changes cannot be attributed cleanly.
Where an external team fits
An outbound support team can manage approved domain and mailbox operations with technical specialists, build and verify lists against written criteria, apply suppression, stage sequences, monitor provider responses, triage replies, route interested prospects and record outcomes in the CRM. Supervision should sample sourcing, messages, classification and compliance.
The client owns positioning, offer, proof, target-account judgement, legal approval, sensitive objections and the sales conversation. It must respond quickly to positive replies and feed acceptance or rejection reasons back to the team. A provider cannot repair an offer nobody wants or make an unqualified list lawful.
Require ownership and exit terms for domains, DNS, mailboxes, provider accounts, lists, suppression, copy, reply history and CRM records. Remove access and stop automation before an engagement ends. Compare this service with the broader small-business lead generation decision guide if email is only one channel under consideration.
Fix the plumbing, then write the email
Inventory every sending domain and system. Verify SPF, DKIM, DMARC alignment and current Gmail and Outlook requirements. Audit source and suppression records, define a narrow first segment, write the ramp and stop rules, then approve one short, truthful message.
OVELITHUB provides cold email, lead-generation and CRM support through English-first managed teams serving USA, Europe and Middle East markets, with more than 130 projects delivered. Request an outbound deliverability and list review before the next sequence begins.
Keep reading
Related insights
How to Triage Support Tickets
Backlogs are a queue design problem, not an effort problem. See how ticket triage, priority rules and SLA discipline keep customer support…
Sales Admin Tasks to Hand Off First
Reps lose selling hours to quotes, CRM updates and scheduling. See which sales admin tasks to hand off, in what order, and…
Outsourced SDR vs In-House Hiring
Outbound stalls when nobody owns it full time. Compare outsourced sales development with hiring an SDR, and see what each option really…